
CVE-2026-119618: What We Know About the Critical Apache mod_http2 Race Condition
Critical Apache HTTP Server Vulnerability: What Defenders Need to Know On November 11, 2026, the Apache Software Foundation disclosed CVE-2026-119618, a critical race condition in mod_http2, the module that provides HTTP/2 support in Apache HTTP Server. According to Apache’s advisory, the flaw can corrupt heap memory and may lead to remote code execution on the […]
php2shell in Practice: Exploitable, Conditional, and Hard to Mass-Exploit
Cutting Through the php2shell Noise On October 20, details of php2shell, two pre-auth RCE vulnerabilities in the PHP core discovered by Calif (CVE-2026-109618 and CVE-2026-109619), leaked ahead of coordinated disclosure. Advisories listing affected versions followed quickly, along with a flood of PoCs, many AI-generated and non-functional. We waited until we had our own data. This […]
GhostPack Necromancy: Reforging C# Tools with WasmForge
In the previous post we walked through WasmForge, our Go-to-WebAssembly loader that takes existing signatured Go tools and ships them as opsec-safe binaries. This approach doesn’t just apply to Go, however, as there are many languages that can compile to WebAssembly. Another language of interest to us, especially regarding legacy tools which have been over-signatured, […]
FreeBSoD: Leveraging Language Models to Find and Exploit Kernel Bugs (Part 1 of 2)
Overview Earlier this year, a team at Praetorian was building Constantine, our automated 0-day discovery engine. I wanted to find techniques worth folding into it, so on the side I started poking at the FreeBSD kernel with Claude Code, running on Opus 4.6, which was the latest Opus model at the time. A few days […]
Centurion: Bring Your Own Execution Environment
Writing my own virtualized loader is something I’ve been wanting to do since I first read Microsoft’s deep dive on FinFisher’s multi-layered VM obfuscation back in 2018. FinFisher didn’t just use one layer of protection, it implemented a custom virtual machine with 32 opcode handlers, wrapped that in spaghetti code and anti-debug checks, and then buried a second VM […]
Enter the WasmForge: Compiling Sliver into WebAssembly
In our last post we used a Claude skill to systematically beat down VirusTotal detection rates on offensive security tools, with a brief mention of a new loader we’d been using to apply those techniques in bulk. This post is about that loader, which we call WasmForge. WasmForge is, from the user’s perspective, a build […]
When Encryption Isn’t Really Encryption
Discovery During a recent network security assessment, we were working on an environment that was well-hardened – Patching was current, password policies were strong, and network segmentation was in place. So, as part of our enumeration of all network assets, we started looking for default credentials and this led us to multiple Canon enterprise printers […]
500,000 Vulnerabilities, 14 That Matter: How Exploit Chain Analysis Cuts Through the Noise
When 500,000 Findings Hide 14 Real Threats Modern enterprises ingest vulnerability data from dozens of sources: endpoint detection and response platforms, vulnerability scanners, cloud security posture tools, container image scanners. A large organization can easily accumulate hundreds of thousands of individual findings. The standard response is to sort by CVSS score, filter for criticals, and […]
CVE-2026-3630: Critical Buffer Overflow in Delta Electronics COMMGR2 Enables Remote Code Execution
Key Takeaways CVSS v3.1 base score of 9.8 (Critical) with vector CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H, according to the CNA Delta Electronics COMMGR2 contains an out-of-bounds write vulnerability (CWE-787) enabling unauthenticated remote code execution NVD lists the vulnerability as analyzed; vendor advisory Delta-PCSA-2026-00005 is available addressing multiple COMMGR2 vulnerabilities No evidence of active exploitation in the wild; specific affected […]
When HttpOnly Isn’t Enough: Chaining XSS and GhostScript for Full RCE Compromise
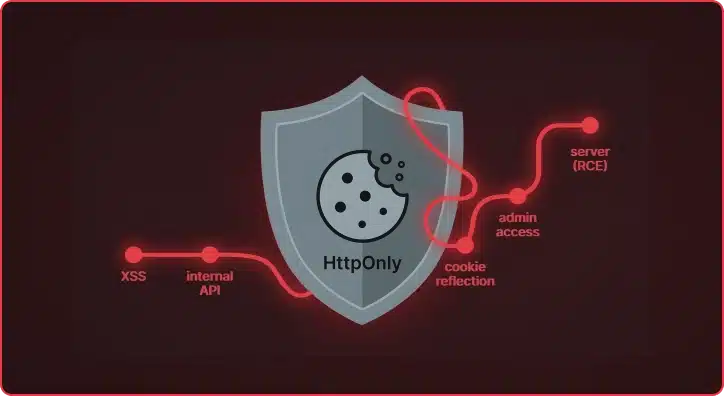
What started as a standard cross-site scripting vulnerability in a document processing platform turned into a full administrative takeover of the application and, ultimately, remote code execution on the underlying server. The HttpOnly flag protected the session cookie from Javascript, but did the application keep it safe? During a recent assessment of a document processing […]